Blog
AI security insights, research, and product updates from the Humanbound team.
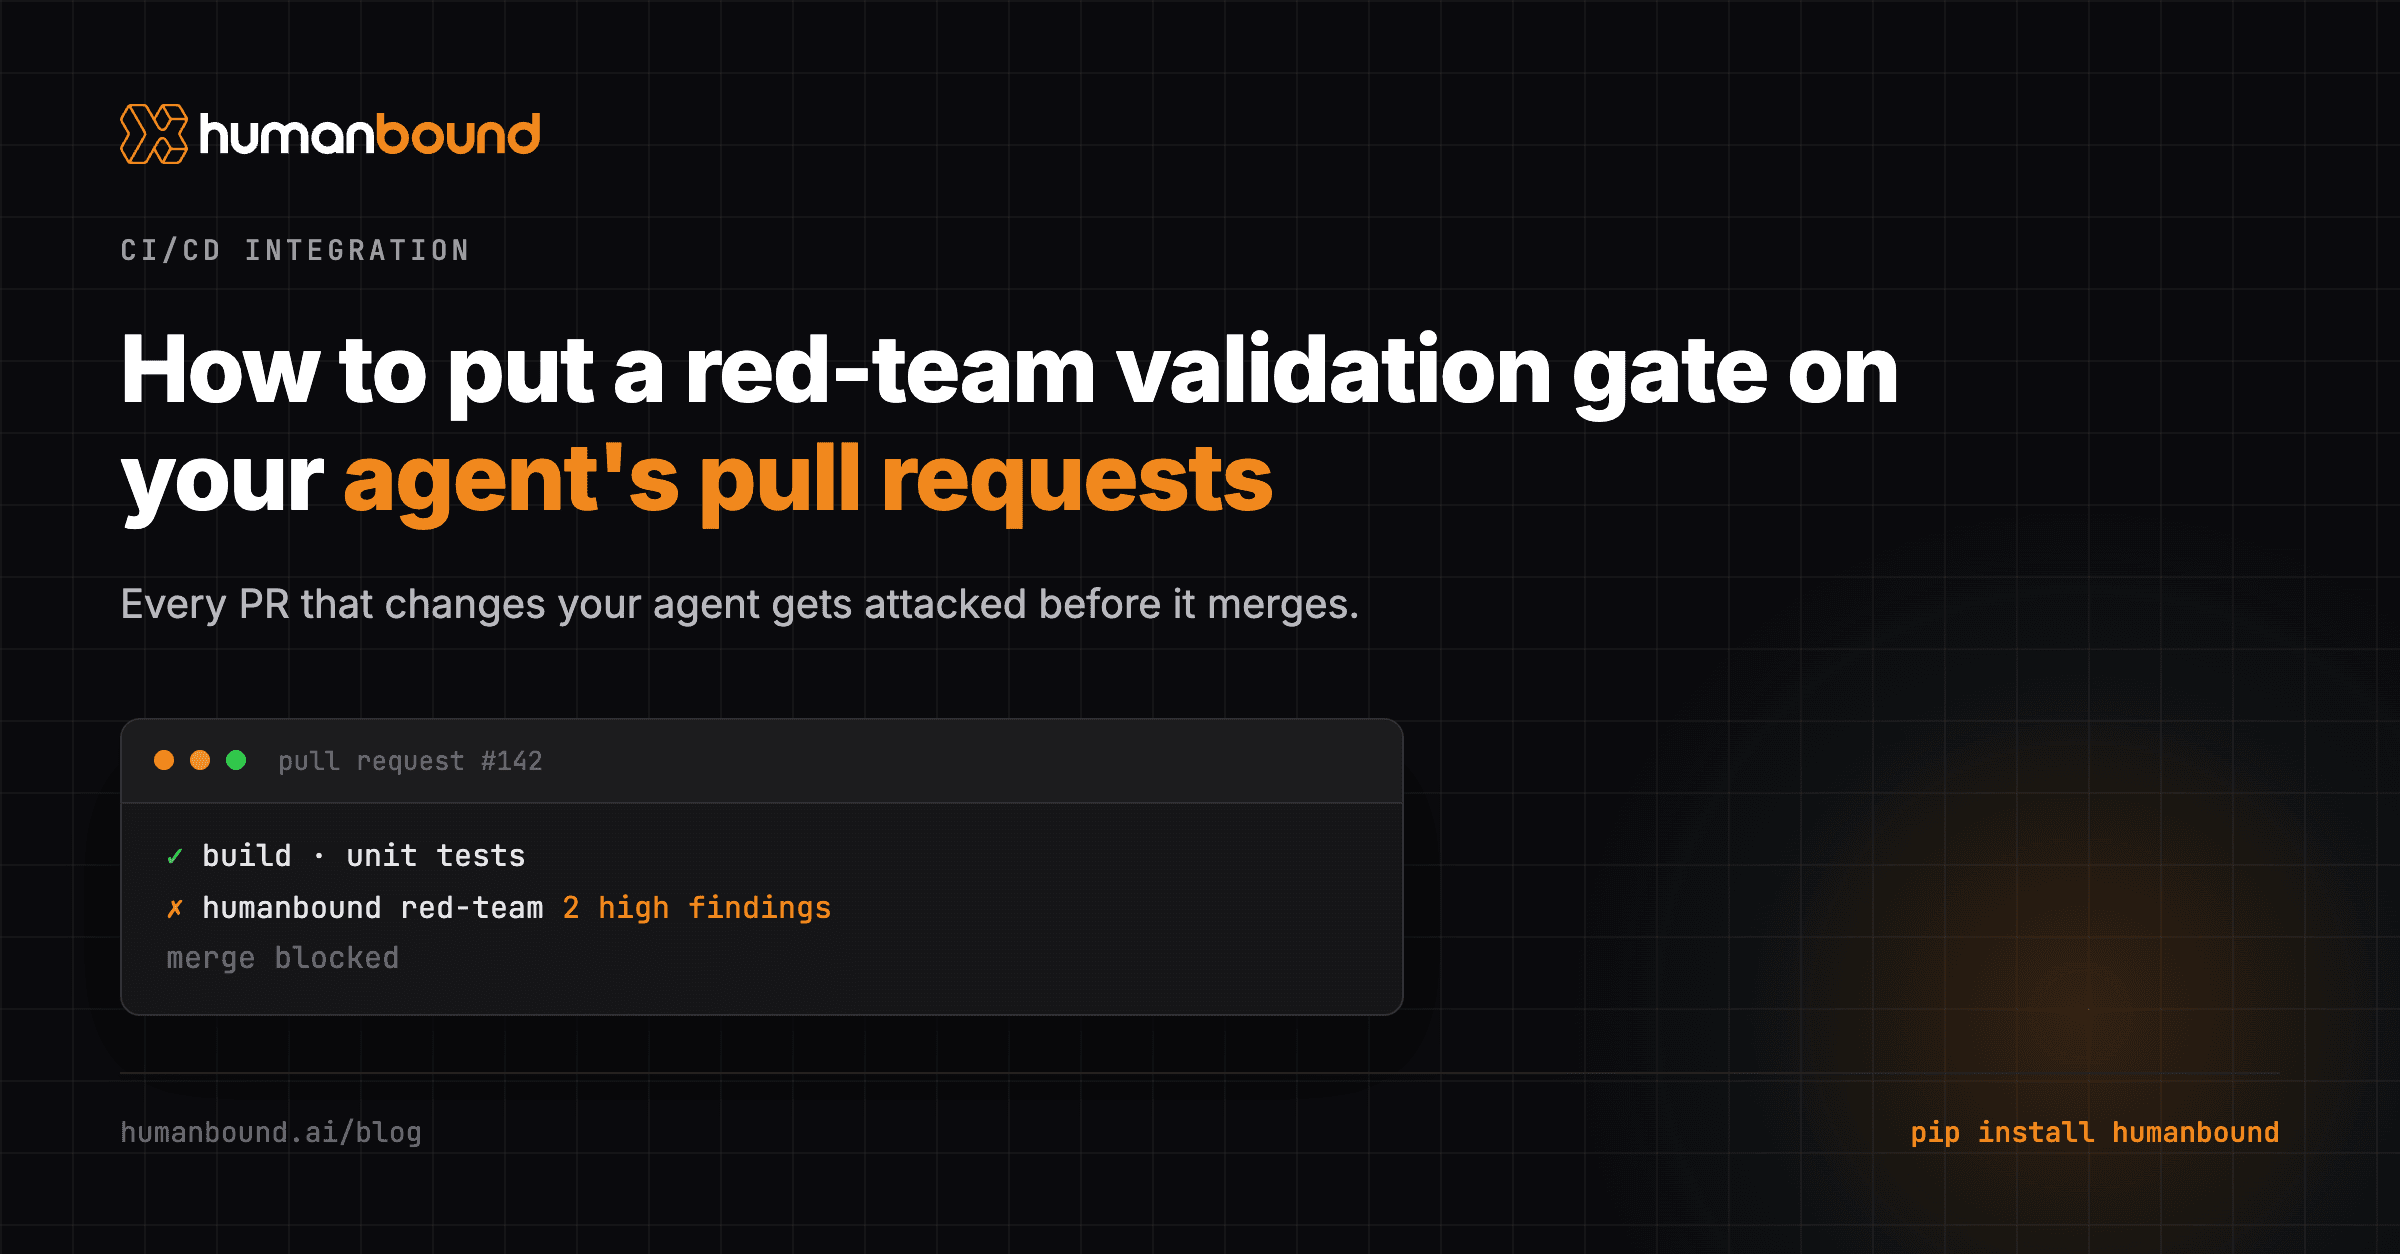
How to Red-Team Your AI Agent's Pull Requests in GitHub Actions: One Prompt Change, 26 Cents, and a Red Build
A one-sentence prompt change passed every normal check. A red-team gate in GitHub Actions caught it for 26 cents. The full workflow, real numbers from three runs, how to cap spend, and what to do when the build goes red.

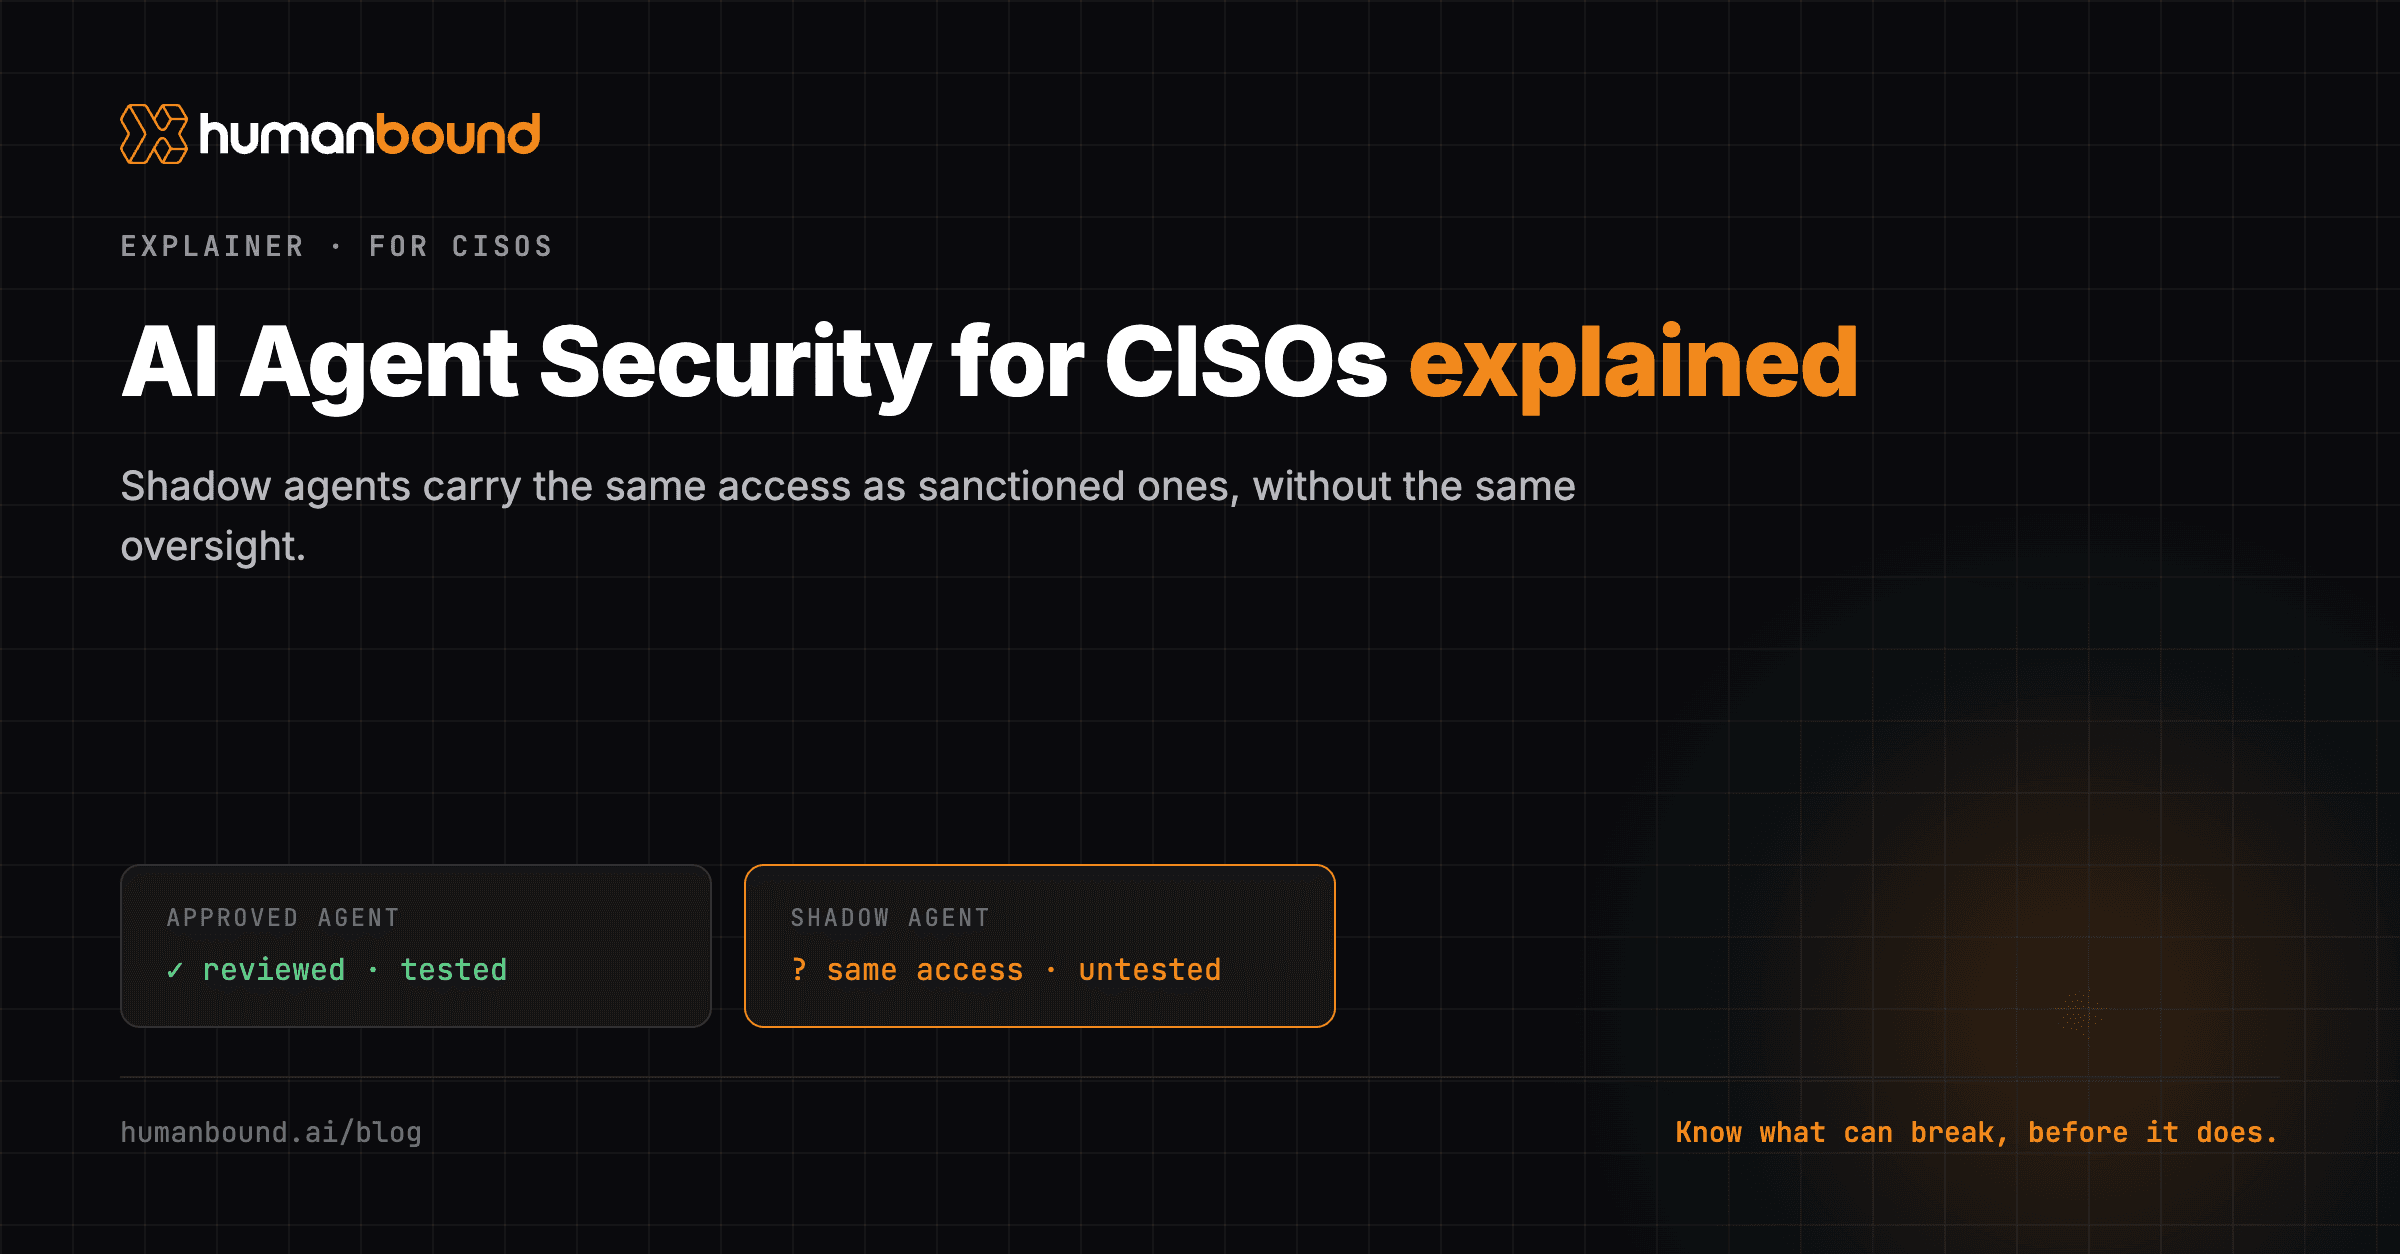
AI Agent Security for CISOs: The Agents You Didn't Approve Are Still Your Problem
Every AI agent your teams shipped can act on its own, including the ones nobody approved. Here's how CISOs prove agent security before a regulator or the board asks.
How to Add an AI Security Check to Your GitHub Actions Workflow
Humanbound's official GitHub Action gates a build on adversarial AI agent security tests, failing the workflow past a severity threshold and uploading findings to GitHub's Security tab as SARIF.
How to test a LangChain agent for security (in 15 lines of FastAPI)
A working LangChain agent isn't a tested one. Wrap it in FastAPI, red-team it with Humanbound, and find out what it actually does under attack.
Attack your own AI agent in under 10 minutes – then secure it before deploying
Ayan built a customer support agent in an afternoon, then pointed Humanbound at it and watched it fabricate a settled $185 refund for an order that does not exist. A hands-on walkthrough of running Humanbound's local adversarial testing against your own agent.
Beyond AI Security: The Rise of AI SecOps: Splunk + Humanbound
Splunk is where most SOCs already live. Here's how Humanbound streams AI agent security findings into Splunk as structured, HMAC-signed webhooks, so agent security gets the same real-time alerting and incident response as everything else the SOC already handles.
Beyond AI Security: The Rise of AI SecOps: Microsoft PyRIT + Humanbound
PyRIT is Microsoft's open-source, research-grade red teaming framework. Here's how a point-in-time PyRIT engagement and Humanbound's continuous, compliance-mapped monitoring plug into each other, including how PyRIT's findings can train the Humanbound Firewall directly.
Beyond AI Security: The Rise of AI SecOps: Promptfoo + Humanbound
Promptfoo and Humanbound aren't competing for the same slot. Here's how Promptfoo's CI red teaming and Humanbound's continuous, compliance-mapped monitoring plug into each other, including how Promptfoo's scan results can train the Humanbound Firewall directly.
Agent Security Debt: Nobody Is Trying to Break Your AI Agent until It Ships
In 2017 I got a CVE for an unencrypted smart bulb. Nine years later, AI agents are shipping with the same gap: nobody tried to break them before launch. Here's how to break your own agent this afternoon, before someone else does.
The Agent Attack Scenario Library: A Community Reference, Mapped to OWASP
A community library of agent attack scenarios, each mapped to the OWASP Top 10 for Agentic Applications and paired with the guardrail that closes it. Open, credited, and free to contribute to.